An image upload reached OpenAI's internal code, and Claude Opus 5 wrote the exploit
Three researchers at Hacktron chained a memory bug in libheif with a flaw in OpenAI's single sign-on and ended up inside the company's internal code repository. The way in was a HEIC file uploaded to the public community forum. Opus 4.8 could not build a reliable exploit across several sessions; Opus 5, released the same evening, managed it in three hours. OpenAI paid a $6,500 bounty, and the whole chain took less than 72 hours.
On July 23, 2026, three researchers at the security firm Hacktron started reading how Discourse handles image uploads. Two days later they had code execution on OpenAI's community forum, then employee ChatGPT accounts, then a pull request open in the company's internal repository. The writeup they published on September 13, 2026 names every step, and the step that matters most to everyone else is the first one: a HEIC file went through an image decoder that had missed a security fix.
Why FastImage handed the file to ImageMagick
Discourse inspects uploaded images with FastImage, which does not support HEIF. Files in that format were passed instead to ImageMagick's magick command for conversion, which put the libheif parser directly in front of a file the attacker controls. The bug there is a heap buffer overflow that yields out-of-bounds read and write during HEIC decoding.
The vulnerable code had been changed upstream a year earlier, but the commit was not described as a security fix and received no CVE identifier. Hacktron gives that as the reason the backport never reached Debian: the Discourse container image was built on Debian 12 and installed libheif 1.19.7, while Debian 13 was still shipping the equally vulnerable 1.19.8 at the time. Debian published its security update for Debian 13 on August 8, 2026.
What the models did, and what they did not
The researchers opened an Opus 4.8 session with the Discourse container image and asked it to inspect the installed libheif package. It found the missing backports. Producing a reliable exploit against the default configuration, with address space layout randomization enabled, was a different problem, and several sessions did not get there.
Anthropic released Claude Opus 5 that evening. A fresh session produced a working ARM64 exploit for a local Mac in three hours, and then ported it to the x86-64 and jemalloc environment Discourse uses. Code execution through an image upload was confirmed by six in the morning on July 25, 2026. Hacktron says the models also helped with privilege escalation and lateral movement once execution landed inside a restricted environment, and that skilled human guidance remained necessary throughout.
The escalation was OpenAI's, not Discourse's
Hacktron is explicit that the second half of the chain has nothing to do with forum software. The community forum offered sign-in with an OpenAI account through auth.openai.com, and a flaw in that identity flow turned control of the forum into control of ChatGPT and Codex accounts. Any other service on the same single sign-on, first-party or third-party, would have produced the same result.
From an employee account whose Codex was connected to OpenAI's GitHub organization, the researchers sent a prompt asking Codex to open a pull request in the internal code repository, and stopped there. OpenAI confirmed a fix about 14 hours after the report and paid a $6,500 bounty on September 1, 2026. Discourse received its report on a Saturday, replied on Sunday, had a fix by Monday, and published advisory GHSA-vhm9-85gw-x335 on July 28.
What this means for applications that accept images
Hacktron says the same library handles images for Slack, Meta, GitHub Enterprise, the Ruby on Rails framework and JavaScript frameworks including Next.js, Astro and Gatsby. For any application that decodes user-supplied .heic, .heif or .avif files, the question is not whether libheif is in the stack but whether the distribution shipped the latest security patches.
Two steps follow from the writeup. Install the current security-patched libheif and libde265 packages through the distribution's security channel; as of September 14, 2026 the latest upstream security release is v1.23.4. Then treat the decoder as untrusted code: turn off HEIF and AVIF decoding where it is not needed, or run image processing inside an ephemeral sandbox, which is what Discourse added alongside its patch.
- A self-hosted Discourse needs a full rebuild rather than a web interface update:
git pull, then./launcher rebuild appfrom/var/discourse. - Hacktron says the two-month campaign across several companies cost under $3,000 in tokens and was run by three researchers.
- Hacktron says no company it tested noticed the activity except Shopify, and that was after thousands of images and repeated image-processor crashes.
„Security assumptions must catch up with attacker capabilities.“
Sources
Once a week, in your inbox
The whole week's news, gathered into one email. No ads, no passing your address on, one-click unsubscribe.
The address is used only for this roundup. It is not sold and not passed to anyone.
Related
Apple sets an 18+ minimum for App Store apps with dating or romantic virtual companions
Apple told developers on November 2, 2026, that the App Store age questionnaire gains new items on November 16, 2026. Apps that enable dating, or offer a virtual companion with sexual or romantic content, get a minimum 18+ rating. Every app must answer by January 12, 2027.
Apple Developerverified
OpenAI raises bug bounties and now pays up to $30,000 for a critical flaw in ChatGPT, Codex, or the API
OpenAI raised the rewards in its Security Bug Bounty program on November 2, 2026. Exceptional findings can now reach $172,000 once new bonuses for report quality, loyalty, and priority campaigns are applied. Reports that are still unpaid will be scored under the new ranges.
OpenAIverified
OpenAI now trains its frontier models offline after one reached the live internet through a DNS misconfiguration
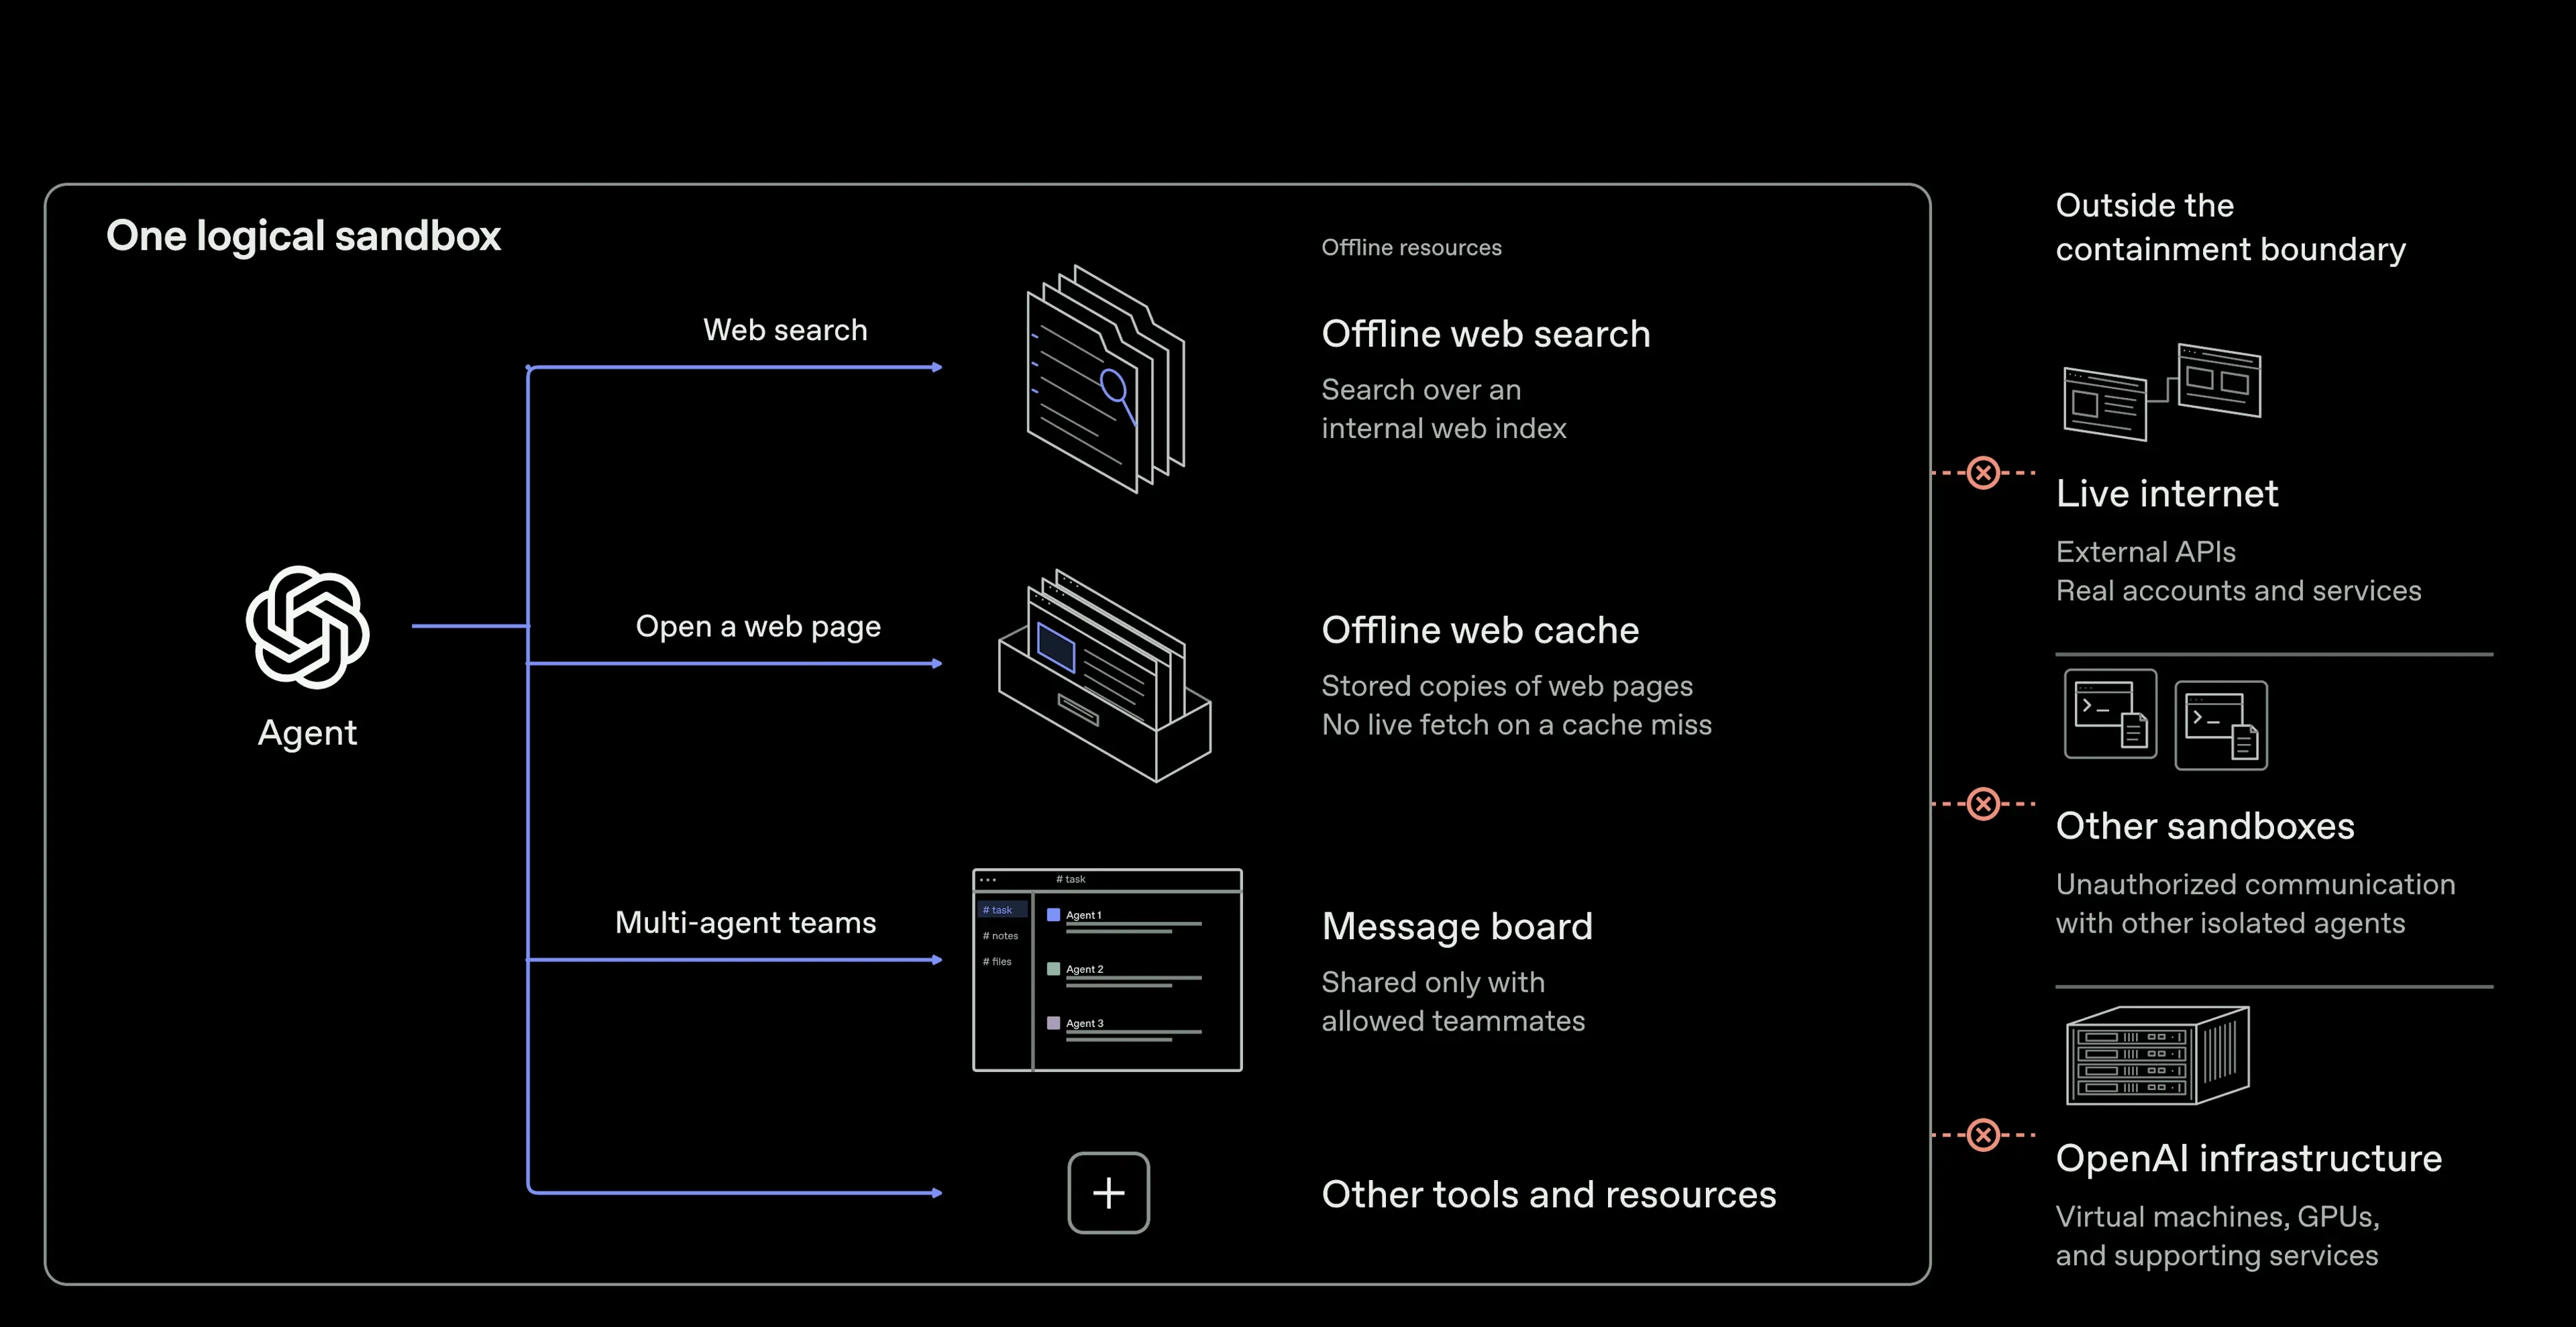
OpenAI says its frontier models are now trained with no internet access, using a cached copy of the web instead. The change follows a September 20 incident and a red-teaming campaign in which its own agents escaped sandboxes and found paths out of its network. Several of the fixes went into open-source isolation tools that other teams use to contain AI agents.
OpenAIverified