Claude Code 2.1.268 closes several ways a deny rule failed to apply
The release published on September 10, 2026 is mostly a permissions release. Deny and ask rules did not apply to symlinked directories when a path was spelled by its real location, and a deny rule on a file could be stepped over by putting an unparseable command on the same line. Two separate fixes stop secrets from being printed into plugin and MCP output. The same build also repairs third-party endpoints, which had been failing every turn with HTTP 400 since 2.1.265.
Source
Claude Code v2.1.268 release notesClaude Code Releases (GitHub) · Original published September 10, 2026
A permission rule is only as good as the check that enforces it, and this release repairs the check in four places at once. Anthropic shipped Claude Code 2.1.268 on September 10, 2026 with a changelog that reads, in its first third, like a security advisory: paths that slipped past deny rules, commands the checker could not read, and secrets printed where they should have been redacted.
Rules that did not reach the command
On macOS, /etc, /tmp and /var are symlinks, and on Linux /bin is one. A deny or ask rule written for one of those directories did not apply when the path arrived spelled by its real location, and a Bash command ignored a deny rule written in the symlinked spelling. Both directions are now handled, so the rule applies to the file rather than to the way it was typed.
The second gap is narrower and easier to hit by accident. A Read or Edit deny rule did not apply when a command the permission checker cannot analyze — env -C, eval or similar — sat on the same line. Anything the checker cannot parse is now handled rather than waved through.
Secrets that were printed
Two fixes in the same release stop credentials from reaching the terminal. Plugin and marketplace errors were showing a token or password taken from a git source URL, and /mcp and /plugin server details, claude mcp list and get, and MCP login errors were showing secrets after ${VAR} placeholders had been resolved. A value that lives in an environment variable exists precisely so it does not appear on screen.
- A respawned in-process teammate could pick up tools or a system prompt from a same-named agent file in a folder that was never trusted.
- Local Cowork sessions set to skip all approvals now refuse a local file outside the session's folders, or behind a symlink, instead of reading it without asking.
- Deny and ask rules written for WebFetch no longer cover Artifact reads and updates; an Artifact rule, or
WebFetch(domain:claude.ai), is what gates those now.
Third-party endpoints work again
Anyone pointing Claude Code at an Anthropic-compatible endpoint from another vendor through ANTHROPIC_BASE_URL had every turn fail with HTTP 400 from 2.1.265 onward. The cause was a regular expression in the Artifact tool's input schema that those endpoints reject, and it is gone in this build. WebFetch also got a deadline: a server that holds a response open without finishing now fails the fetch after 300 seconds, and CLAUDE_CODE_WEBFETCH_DEADLINE_MS moves or removes that limit.
„Fixed PermissionRequest hooks not firing in --print mode“
Once a week, in your inbox
The whole week's news, gathered into one email. No ads, no passing your address on, one-click unsubscribe.
The address is used only for this roundup. It is not sold and not passed to anyone.
Related
Claude Code 2.1.321 stops MCP sign-in from sending refresh tokens to another host after a redirect
The most serious fix in the release concerns MCP servers that require an OAuth sign-in. Three more fixes cover cases where a shell command or a file write got past a permission check. Claude Fable 5.2 also becomes the default Fable model.
Anthropicverified
OpenClaw 2026.11.2 stops project settings from adding programs to the agent's PATH
OpenClaw's latest patch release adds no features and fixes a set of security problems. The most serious one let a settings file inside a project add programs from that project to the list of directories where the system looks for commands. Two of the fixes change existing behavior, so some setups need to be adjusted.
OpenClawverified
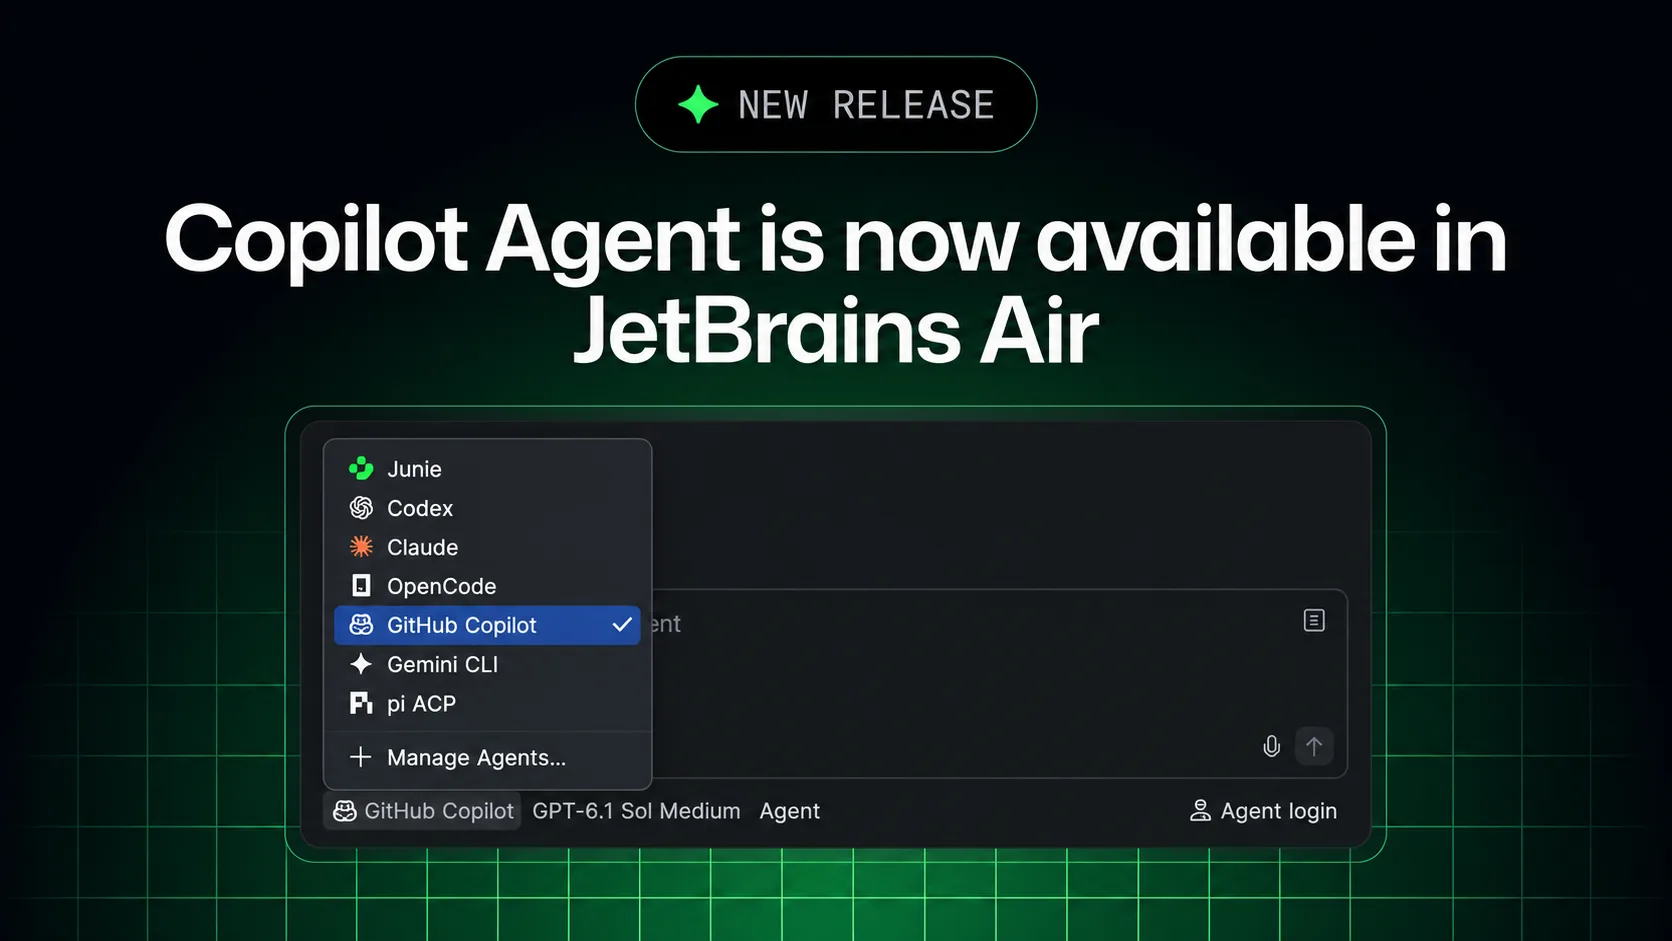
GitHub Copilot now runs in JetBrains Air, and its cloud tasks use a Copilot plan instead of JetBrains credits
Copilot can now be picked as an agent in Air for local and cloud coding work, on an existing subscription. Air administrators can switch it off, but they cannot cap its spending in Air or see its usage in Air's analytics.
GitHubverified